I remember the initial time I attempted to log into an online casino. The form seemed simple: two fields and a button. Behind it lay a layered system juggling speed and security. As a technical writer, I have dedicated years examining how authentication flows truly work. A casino login page is by no means just a door. It is a checkpoint where identity verification, session management, fraud detection, and regulatory compliance meet in milliseconds. Let me walk through the real mechanics of casino login options, from typing your credentials to the moment the dashboard loads. I will explain sign-up steps, verification layers, and security measures that safeguard your funds and personal data without you being aware.
Verification of Identity and KYC Procedures
Identity verification, often called KYC or Know Your Client, is a procedure that a lot of players encounter after their initial major win or withdrawal request. I have realized that it is not a punishment but a regulatory requirement that casinos must fulfill. When I am required to upload documents, I usually provide a government-issued identification, a current utility bill or bank record indicating my address, and sometimes a image of the payment method I used. The casino’s regulatory team reviews these documents to confirm that I am the individual I say I am and that I am not employing someone else’s identity. The check can last anywhere from a few hours to a few days, based on the number of requests and the clarity of my files.
From a technological viewpoint, I am impressed by how current casinos mechanize parts of this procedure. Text recognition software pulls my personal details from the uploaded images, and liveness detection algorithms check that the selfie I submit matches the picture on my ID and is not a static image. The system then matches my data against worldwide databases. Once verified, my profile status is improved, and my cash-out limits are typically increased. This authentication is a one-time process; after I finalize it, my upcoming logins remain unaffected, and I can conduct transactions without restrictions. I always make sure my files are clear and valid because refused submissions only hold up access to my money. The security benefit is mutual: authenticated accounts are less susceptible to fraud, and my personal account recovery becomes easier because the casino has a verified identity on file.
Two-Factor Authentication and Biometric Authentication
Two-factor authentication, WinnItt connexion sécurisée, or 2FA, is the most effective security upgrade I can activate on my casino account. When I turn on 2FA, logging in demands my password plus a one-time password generated by an authenticator app on my phone. The algorithm behind this, typically TOTP, synchronizes a mutual key between the server and my device, producing a new six-digit code every thirty seconds. Even when someone captures my password, they cannot log in without possession to my phone. Some casinos provide 2FA via SMS as well, but I favor app-based codes because SMS messages can be intercepted through SIM-swapping attacks. The setup process is straightforward: I scan a QR code, and my authenticator app starts generating codes immediately.
Biometric authentication adds another aspect that I find both easy and protected. On mobile devices, I can often log in using my fingerprint scan or facial recognition instead of typing a password. This is not to say the casino stores my fingerprint data. The biometric sensor on my device performs the match locally and then releases a cryptographic key that authenticates me to the server. The FIDO2 standard governs much of this process, and my biometric template never leaves my device. For casino platforms, biometric login decreases friction significantly while keeping strong security. Some operators integrate biometrics with device binding, so the login only works from my registered phone, adding another tier of protection against remote attacks.
Login Recovery and Security Recommendations
I have been locked out of online accounts previously, so I pay close attention to how a casino processes account recovery. The typical recovery flow begins with a “Forgot Password” link on the login page. When I click it, I am required to enter my registered email address. The system then sends a time-limited reset link or a code to that email. Secure casinos rarely reveal whether an email address is stored in their database during this step, preventing attackers from harvesting valid usernames. The reset link itself features a cryptographically random token that expires quickly, usually within 15 to 30 minutes. Once I establish a new password, all existing sessions are revoked, which secures me if someone else was already accessing my account.
Beyond password resets, I have implemented several habits that strengthen my login security. I employ a password manager to produce and save unique credentials for every casino, so a breach at one site does not compromise others. I also turn on login notifications wherever possible, getting an email or push alert each time my account is used from a new device or location. This offers me an early warning if something unusual occurs. I frequently examine my active sessions in the account settings and close any I do not identify. Finally, I ensure my contact information updated, because the casino may use my phone number or email for critical security alerts. These habits, combined with the platform’s own defenses, establish a defense-in-depth strategy that ensures my funds and personal data secure every time I log in.
Traditional Username and Password Access
The username and password combination stays the most common casino login method, and I have studied its strengths and weaknesses extensively. When I create a password during sign-up, the casino never stores it in plain text. Instead, the system processes my password through a cryptographic hashing algorithm such as bcrypt or Argon2, which transforms it into a fixed-length string that cannot be reversed. Even if a database breach took place, attackers would only acquire these hashes, not my actual password. I always suggest using a unique, long passphrase because the hashing process makes guessing computationally expensive. Casinos that adhere to modern security standards also salt each hash, adding random data before hashing so that two users with the same password produce different hashes.
From a usability perspective, many players face password fatigue. That is why casinos progressively implement passwordless alternatives, but the traditional method persists because everyone comprehends it. When I log in with my credentials, the server checks the hash of what I typed with the stored hash. If they match, the system creates a session token, usually a JSON Web Token or a random session ID stored in a secure HTTP-only cookie. This token tracks me as I navigate the site, confirming my identity without requiring me to re-enter my password on every page. I consider this session management layer just as critical as the initial authentication, because a stolen session token can be as damaging as a stolen password.
The Structure of a Casino Login Form
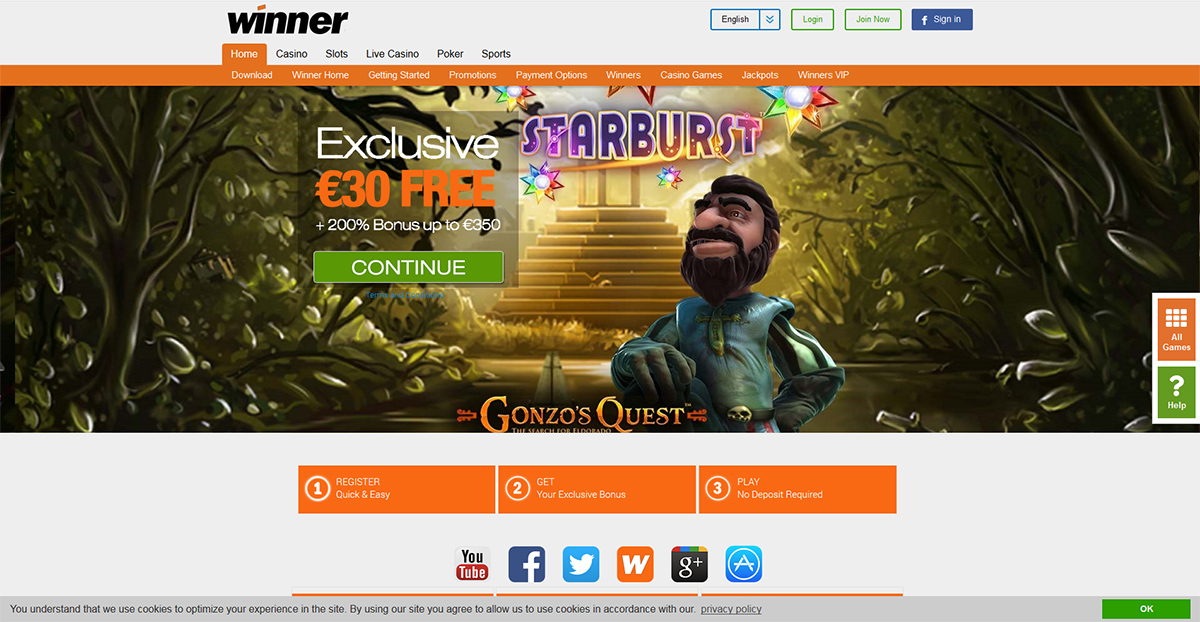
When I examine a casino login page like the one at WinnItt Casino, I notice a carefully engineered interface. The visible part typically includes two input fields for an email or username and a password, a login button, and a few auxiliary links for password recovery or account creation. Beneath that surface, the page loads scripts that set up a secure session. The form is wrapped in HTTPS encryption, which I can check with the padlock icon in my browser. This encryption jumbles every character I type before it travels across the network. The login endpoint also includes a CSRF token, a hidden field that blocks malicious sites from submitting requests on my behalf. Reputable casinos always implement these fundamentals before adding any advanced options.
What I find fascinating is how the form responds to my behavior. If I mistype my password several times, the system may temporarily suspend my account or present a CAPTCHA challenge. This is not a random annoyance; it is a rate-limiting mechanism that prevents automated brute-force attacks. Behind the scenes, the server logs each attempt and determines a risk score based on my IP address, device fingerprint, and login history. If the score exceeds a threshold, the casino might silently step up security, perhaps requiring an additional verification code sent to my email or phone. These checks happen without crowding the interface. The design philosophy remains clear: keep the visible login form minimal while the backend handles complexity.
Social Authentication and SSO Connections
Social login buttons are now standard on many casino registration pages, and they transform the authentication dynamic significantly. When I decide to log in with a Google or Facebook account, I am delegating identity verification to a third-party provider. The casino never views my social media password. Instead, the provider transmits a signed token that confirms my identity and, if I consent, provides basic profile information such as my email address and name. This flow is based on the OAuth 2.0 protocol, which I have set up in test environments and deem reliable when configured correctly. For me, the primary advantage is speed; I can complete the sign-up and login process in a few clicks without creating another set of credentials.
But I also recognize the trade-offs. When I use social login, my casino account becomes linked to my external profile. If that external account is compromised, an attacker could potentially access my casino balance. That is why I always turn on two-factor authentication on my social accounts before using them for casino access. Some casinos still ask me to set a separate withdrawal password or PIN even after social login, offering a financial safety net. From a technical standpoint, the casino’s backend must process token validation, expiration, and revocation properly. I have seen poorly implemented OAuth integrations that kept sessions dangling, but reputable operators like WinnItt Casino maintain tight integration with identity providers, ensuring tokens are verified on every request.
The Sign-Up Flow and Registration Steps
When I sign up for a new casino account, the sign-up flow is beyond a data collection form; it is the basis of my future login experience. The first step typically requests an email address, a password, and my chosen currency. I always pay close attention to the password strength meter, which evaluates complexity in real time by checking length, character variety, and common patterns. After submitting the initial form, I usually receive a verification email that includes a link or a numeric code. This step confirms that I own the email address and avoids typos that could lock me out later. I consider email verification non-negotiable because it also serves as a recovery channel if I forget my password.
The next stage typically requires personal details such as my full name, date of birth, and residential address. This information is not only for marketing; it is needed by anti-money laundering regulations and licensing conditions. The casino cross-references my data against sanctions lists and politically exposed persons databases in real time. I have encountered systems that can finish these checks within seconds, allowing me to proceed to the deposit screen almost immediately. Some platforms also ask me to set security questions during sign-up, but I handle those cautiously. I view security answers as additional passwords and never use real information that could be inferred from my social media. Once the registration is complete, my login credentials are entirely active, and I can enter the cashier and game lobby.